Demonstrate
Security & Resilience
to Enterprise Buyers.
Show that your cloud and SaaS platforms operate with strong, tested controls across security, availability, confidentiality, and related trust principles.
Meeting TSC Standards for
Cloud & SaaS Providers
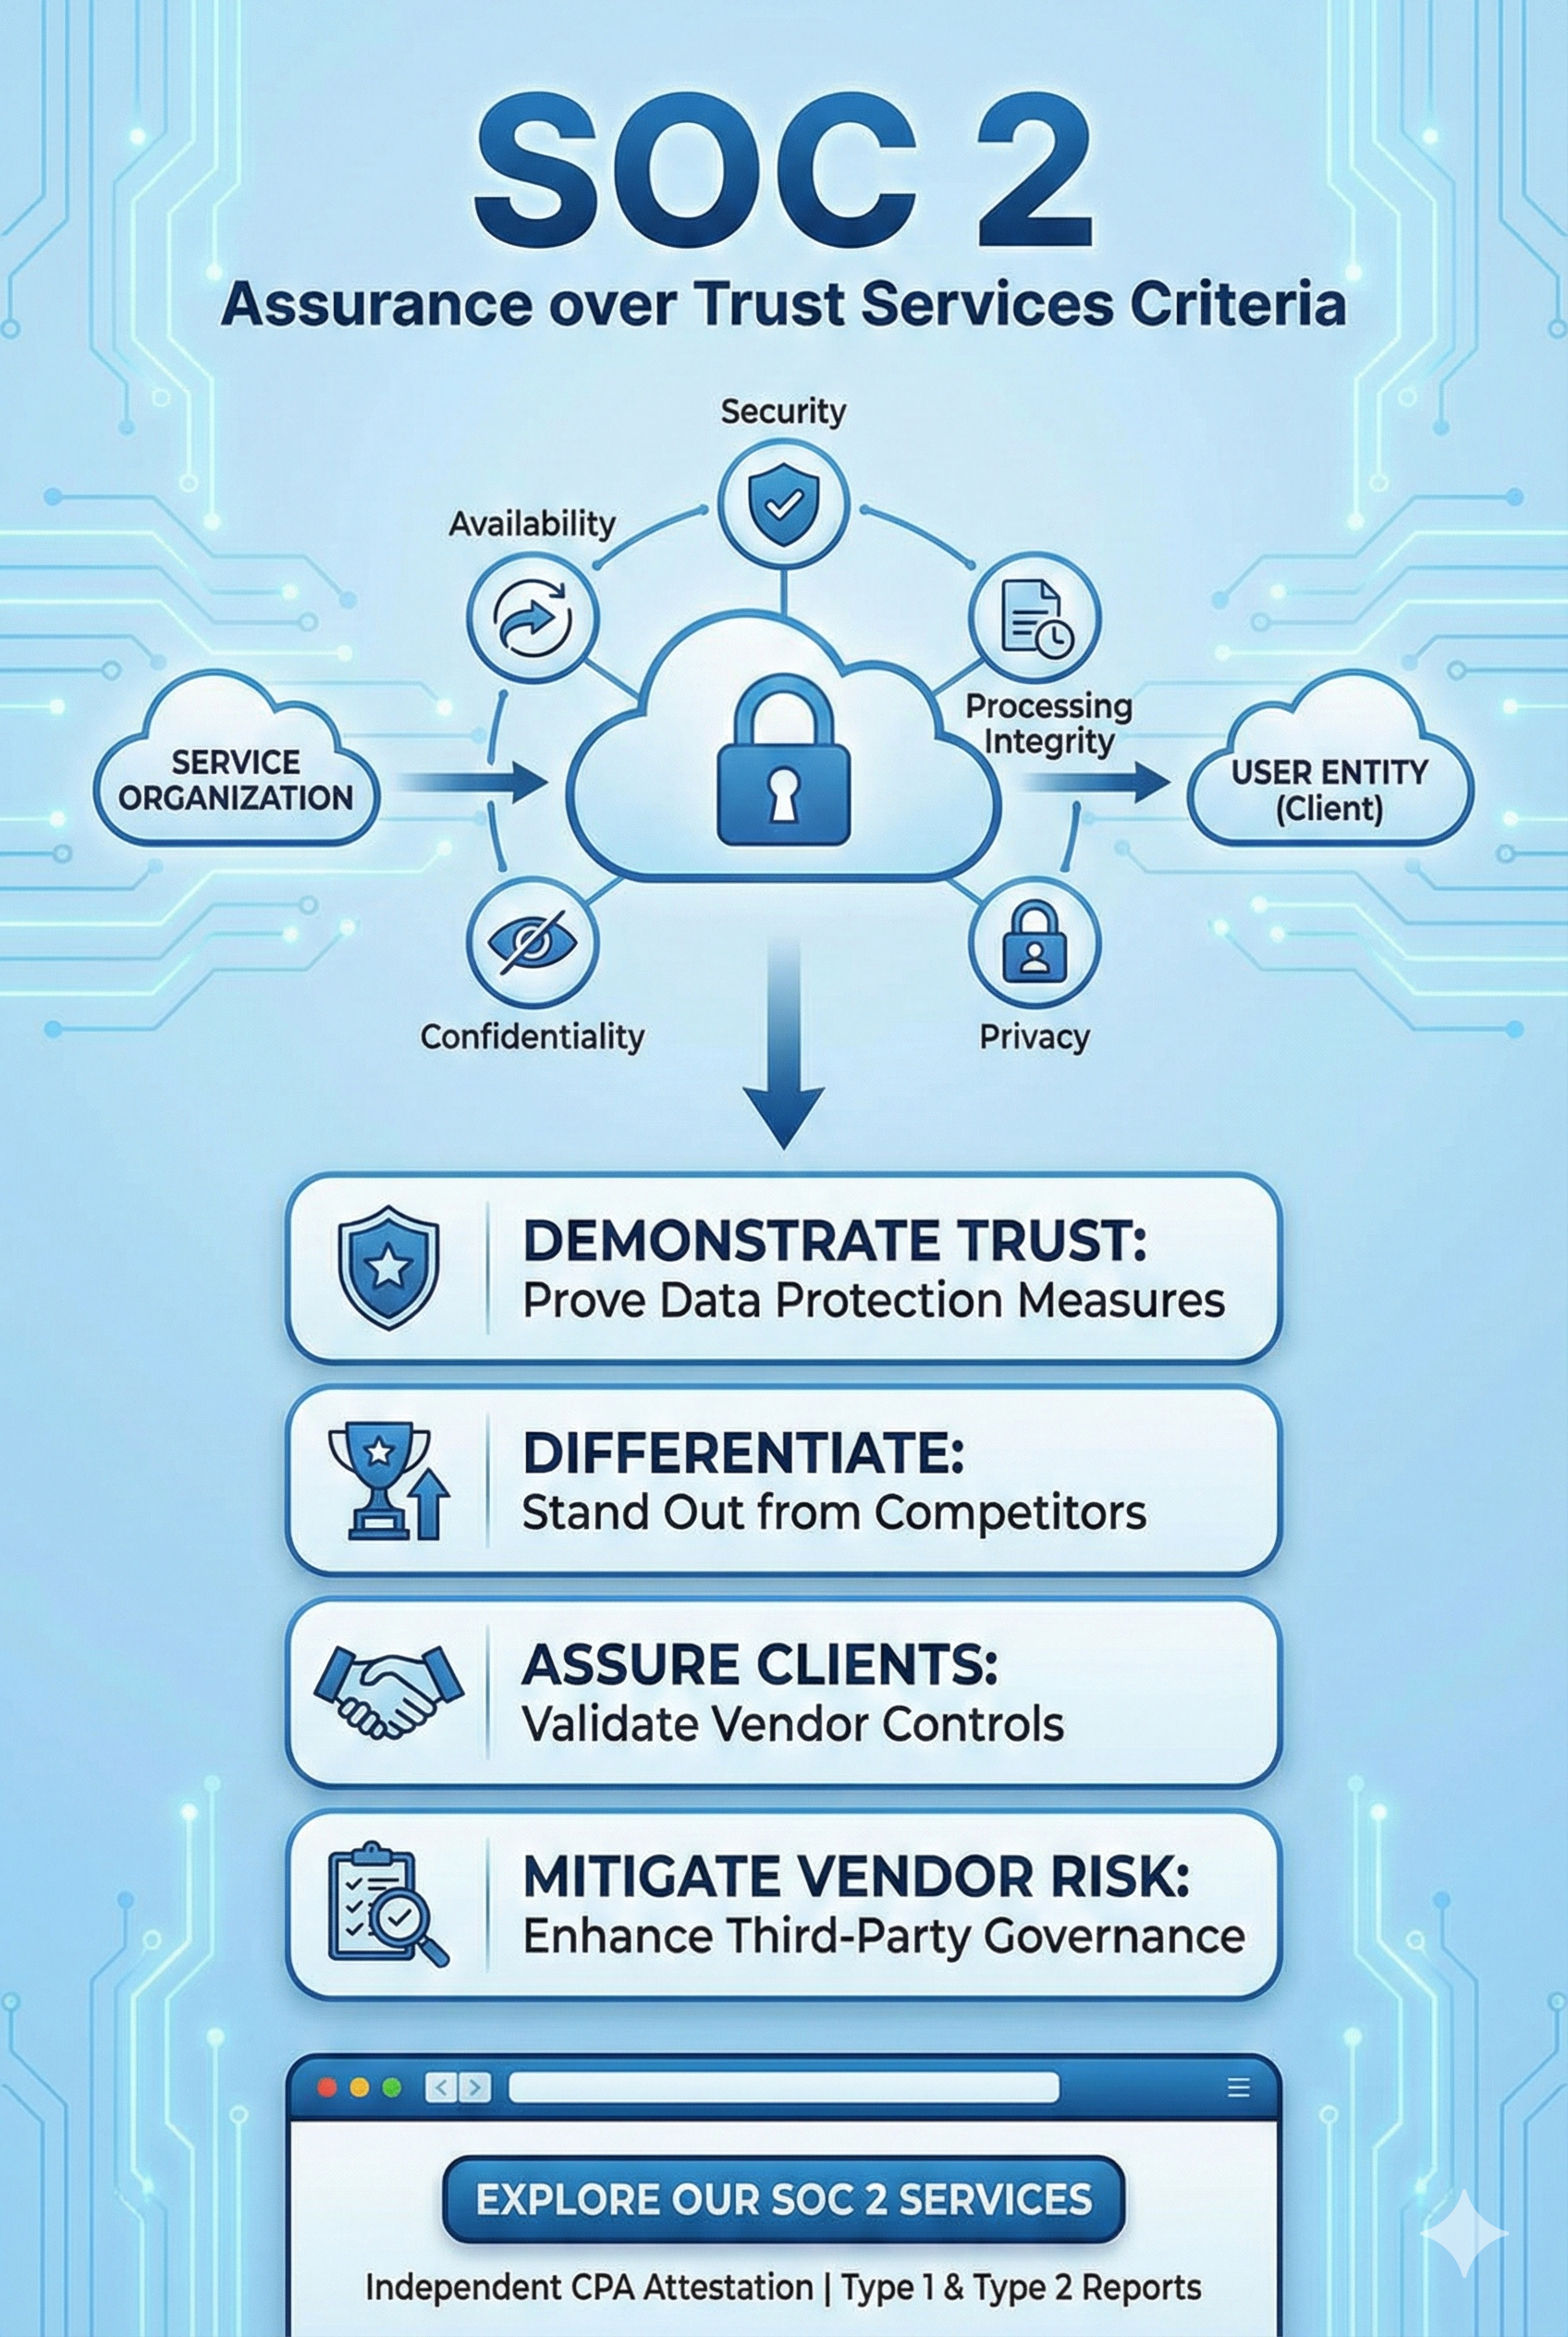
SOC 2 In One View
SOC 2 focuses on security plus the selected Trust Services Criteria—availability, processing integrity, confidentiality, and privacy. Security is mandatory and included in every SOC 2 report.
"This framework is best suited for SaaS, cloud, data processing, and technology-driven services. The output is a detailed report for customers’ security and risk teams under NDA."
SaaS
Cloud
Data Centers
Tech Services
Trust Services Criteria
Security
Protection against unauthorized access and use.
Availability
Uptime, resilience, disaster recovery capabilities.
Processing Integrity
Accurate, complete, timely, authorized processing.
Confidentiality
Protection of sensitive information from disclosure.
Privacy
Handling personal data in line with regulations.
Why SOC 2 Is Now a Sales Prerequisite
Enterprise buyers make SOC 2 Type II a condition for onboarding.
Shortens security due diligence and reduces long questionnaires.
Signals a mature security posture to boards and investors.
Supports vendor risk management and cyber insurance.
SOC 2 Type I
Snapshot of control design at a specific date.
First MilestoneSOC 2 Type II
Evidence of design and operating effectiveness over 6–12 months.
Market StandardMany growing companies start with Type I and progress quickly to Type II.
RiskMan SOC 2 Support
Readiness Reviews
Governance, access, change control, and incident response audits.
Remediation
Prioritised plans aligned with your product roadmap.
Evidence Strategy
Repeatable audit strategies that are less disruptive.
Ongoing Advisory
Keep SOC 2 aligned with evolving customer expectations.
Frequently Asked Questions
Why Do Enterprise Customers Insist on SOC 2 Type II?+
Type II proves that controls not only exist but have operated effectively over time, which is crucial for always-on services.
Can We Limit SOC 2 Scope to Specific Products?+
Yes. You can scope SOC 2 to particular services or environments, clearly described in the system description.
Does SOC 2 Cover Data Residency and Privacy Laws?+
Privacy criteria can address personal data handling; however, SOC 2 should be aligned with specific regulatory requirements separately.
What Are Common Gaps Found During SOC 2 Readiness?+
Missing policies, inconsistent access reviews, manual processes lacking evidence, and incomplete vendor risk management are typical gaps.
How Do We Maintain SOC 2 Between Audits?+
By operating controls continuously, regularly reviewing evidence, and tracking remediation of issues throughout the year.
Make SOC 2 A Growth Enabler, Not A Checkbox
Use SOC 2 to remove security as a sales blocker and position your service as a low-risk, high-trust choice.