SOC 1 Assurance for
Financial Reporting
Reliability.
Reassure customer CFOs and auditors that outsourced processes supporting financial statements are controlled, tested, and independently verified.
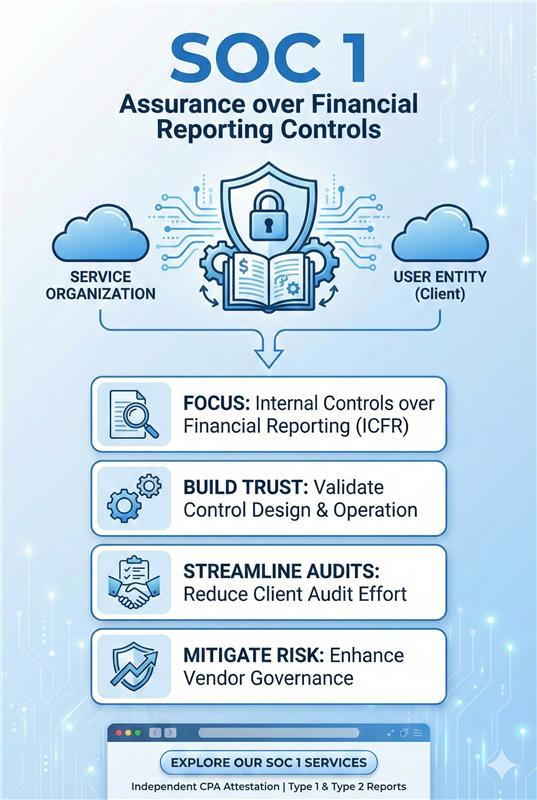
SOC 1 In One View
SOC 1 focuses on controls that impact our customers’ financial reporting. Typical users include CFOs, controllers, and external auditors of our clients.
The Core Outcome
The primary result is reduced duplicate testing and smoother external audits for our customers. It builds a bridge of trust between your operations and their finance departments.
Type I
Point in TimeIndependent opinion on control design accuracy at a specific date. Useful for initial baseline assessments.
Type II
6–12 Month PeriodOpinion on design and operating effectiveness over time. This is the market expectation for mature providers.
Key Benefits for Organizations
Audit Ready
Easier to audit and work with large-scale enterprise customers.
SOX Support
Supports statutory audit requirements, improving client retention.
Save Time
Reduce management time spent on bespoke control testing requests.
Governance
Demonstrate disciplined governance over financial operations.
RiskMan SOC 1 Services
Scope Definition
Aligned to financial reporting impact and customer expectations.
Readiness Assessment
Identify control gaps across processing, access, and change management.
Remediation Guidance
Documentation support and evidence coaching for your teams.
Audit Coordination
Seamless examination coordination with independent auditors.
Outcomes You Can Expect
"A mature SOC 1 posture translates into lower audit friction, higher confidence from customer finance leaders, and stronger positioning in competitive RFPs."
Repeatable Asset, Not A One-Off Effort
Frequently Asked Questions
When Is SOC 1 More Appropriate Than SOC 2?+
SOC 1 is appropriate when your services can materially affect customers’ financial statements, and their auditors rely on your controls.
How Does SOC 1 Support Our Customers’ SOX Programs?+
Your SOC 1 report allows customer auditors to rely on your controls instead of re-testing them extensively in your environment.
Do All Services We Offer Need to Be in Scope?+
No. Scope is limited to services and systems that impact customers’ financial reporting, agreed with auditors and key clients.
What Is Typical SOC 1 Control Areas?+
Processing accuracy and completeness, logical access, change management, incident handling, and reconciliations for in-scope systems.
Is SOC 1 A One-Time Project?+
No. It is an annual cycle that embeds control discipline into ongoing operations and relationships with customers’ auditors.
Give Your Customers’ Auditors Fewer Reasons to Say No
Use SOC 1 to prove that the financial processes you run for customers are controlled, tested, and reliable.